Cipher Visualizers home

Tag

#Cryptanalysis

35 articles with this tag.

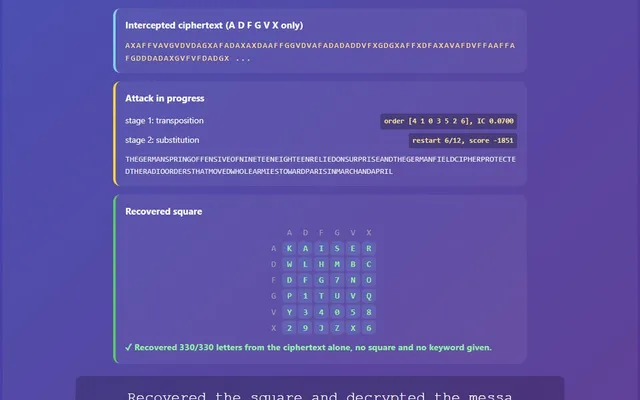
A visual representation of recovering the ADFGVX transposition and substitution to decrypt a message
Basic Classic Symmetric Breakers Advanced

Breaking the ADFGVX Cipher

ADFGVX fractionates each letter into two symbols and then shuffles them with a columnar transposition, the combination that made it Germany's toughest field cipher of 1918. This guide runs the modern automated attack: recover the transposition with the index of coincidence, then solve the substitution with quadgrams, and read a 330-letter message back out.

14 min read
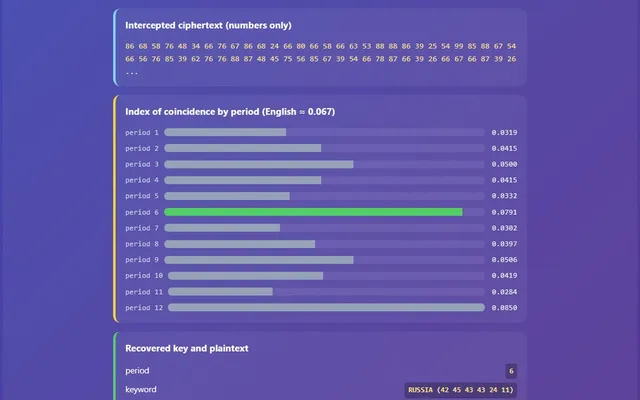
A visual representation of index-of-coincidence period finding and column key recovery against the Nihilist cipher
Basic Classic Symmetric Breakers Intermediate

Breaking the Nihilist Cipher

The Nihilist cipher turns letters into Polybius numbers and adds a repeating keyword, which makes it a Vigenere cipher wearing a numeric disguise. Index of coincidence finds the period, and column-by-column statistics peel off the key. This guide runs the real attack and recovers a 514-letter message.

13 min read

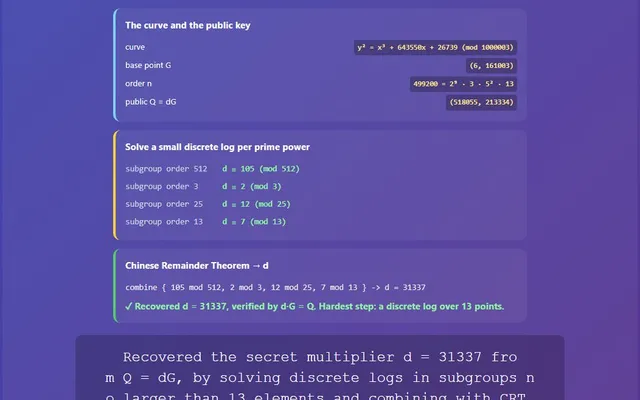
A visual representation of Pohlig-Hellman splitting an elliptic curve discrete log into small subgroups and combining with CRT
Modern & Applied Cryptography Breakers Advanced

Breaking Toy ECC with Pohlig-Hellman

Elliptic curve security does not come from the size of the field. It comes from one number: the largest prime factor of the group order. When that order is smooth, Pohlig-Hellman splits the discrete log into tiny subgroups and solves it in a flash. This guide runs the real attack on a toy curve and recovers the private key.

13 min read

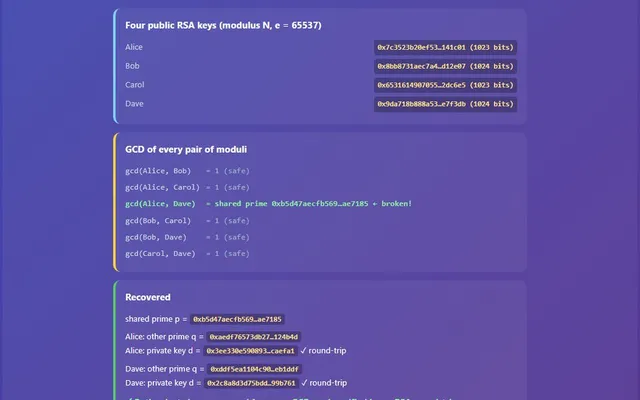
A visual representation of a batch GCD finding a shared prime between two RSA moduli and factoring both
Modern & Applied Cryptography Breakers Advanced

Breaking RSA with Weak Keys: Shared Primes and Pollard's p-1

RSA is unbreakable only when its primes are chosen well. If two keys share a prime, one GCD factors both in microseconds, and if a prime p has a smooth p-1, Pollard's method factors it without any search. This guide runs both real attacks against real 1024-bit keys and recovers the private keys.

11 min read

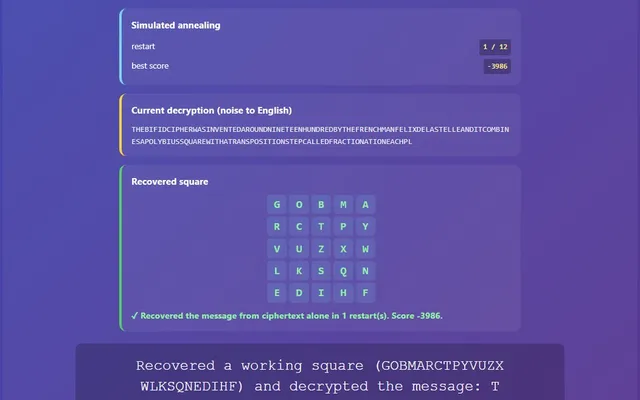
A visual representation of simulated annealing recovering a Bifid Polybius square from ciphertext
Basic Classic Symmetric Breakers Advanced

Breaking the Bifid Cipher with Simulated Annealing

Bifid fractionates each letter into coordinates and shuffles them, which hides single-letter frequencies. Given the period, a hill climb over the Polybius square guided by English quadgram statistics peels the key apart anyway. This guide runs the real attack and recovers a 669-letter message.

13 min read

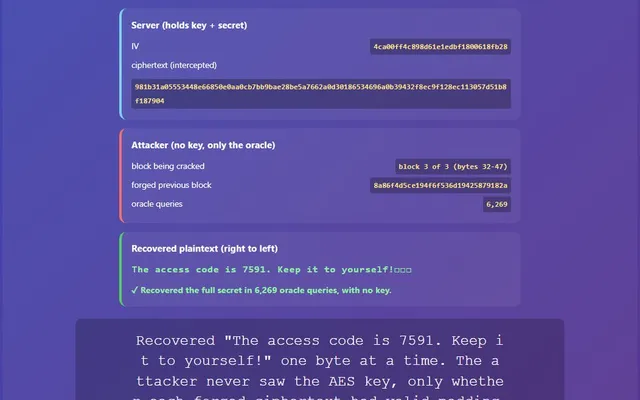
A visual representation of the padding oracle attack recovering AES-CBC plaintext one byte at a time
Modern & Applied Cryptography Breakers Intermediate

Breaking AES-CBC with a Padding Oracle

A server that only tells you whether decrypted padding was valid hands you the whole plaintext. This guide runs the real CBC padding-oracle attack against full AES-128, recovers a secret message one byte at a time, and explains why POODLE and Lucky 13 made authenticated encryption the rule.

16 min read

A visual representation of the meet-in-the-middle attack recovering two DES keys
Modern & Applied Cryptography Breakers Intermediate

Breaking Double DES with Meet-in-the-Middle

Encrypting with DES twice looks like it should double the key to 112 bits. A meet-in-the-middle attack shows it barely adds one bit of real security, which is why 3DES uses three passes. Learn the attack with runnable Python against real DES.

12 min read

A visual representation of the four-square cipher breaker recovering two key squares
Basic Classic Symmetric Breakers Advanced

Breaking the Four-Square Cipher with Two Key Squares

The four-square cipher hides letter frequencies behind two keyed grids, but it is still a pencil-and-paper cipher. Learn how simulated annealing with quadgram statistics recovers both secret squares from the ciphertext alone, with runnable Python.

14 min read

A visual representation of a hash length-extension attack forging a message authentication tag
Modern & Applied Cryptography Breakers Intermediate

Forging MACs with a Hash Length-Extension Attack

Using a plain hash as a MAC, with tag = H(secret || message), is a classic mistake. A length-extension attack appends your own data and forges a valid tag without ever knowing the secret. Learn the attack on SHA-256, with runnable Python, and why HMAC exists.

11 min read

A visual representation of the many-time-pad attack recovering reused-key messages
Basic Classic Symmetric Breakers Intermediate

Breaking the One-Time Pad by Reusing Its Key

A one-time pad is unbreakable, but only if the key is used once. Reuse it across several messages and the key cancels out. Learn the many-time-pad attack and crib-dragging, with Python that recovers the messages from the ciphertexts alone.

14 min read

A visual representation of recovering an ECDSA private key from two signatures that reused the same nonce
Modern & Applied Cryptography Breakers Advanced

Recovering a DSA or ECDSA Key from a Reused Nonce

DSA and ECDSA stake everything on a secret random nonce that must never repeat. Sign two messages with the same nonce and the private key drops out with a little algebra. This guide runs the real attack against real DSA and secp256k1, the same flaw that broke the PS3 and drained Bitcoin wallets.

12 min read

A visual representation of four different TEA keys that all encrypt the same plaintext to the same ciphertext
Modern & Applied Cryptography Breakers Intermediate

TEA's Equivalent Keys and the Xbox Hack

Every TEA key has three twins that encrypt identically, because flipping the top bits of two key words cancels in the round function. That one-bit quirk shrank TEA's key to 126 bits and let hackers forge a hash to break the original Xbox. This guide runs the real thing against real TEA.

12 min read

A visual representation of the two-square cipher breaker recovering two key squares from a crib
Basic Classic Symmetric Breakers Advanced

Breaking the Two-Square Cipher with a Crib

The two-square cipher resists the ciphertext-only search that breaks Playfair and four-square, because it has no fixed reference squares. But a crib of known plaintext breaks it in seconds. Learn the known-plaintext attack, with runnable Python.

13 min read

A visual representation of the FMS attack voting to recover each byte of a WEP key from weak IVs
Modern & Applied Cryptography Breakers Advanced

Breaking WEP with the FMS Attack on RC4

WEP bolted RC4 onto a 3-byte IV sent in the clear, and that choice was fatal. The Fluhrer-Mantin-Shamir attack recovers the shared key from the first byte of thousands of weak-IV packets. This guide runs the real attack against real RC4 and recovers the key byte by byte.

14 min read

A visual representation of breaking DES by exhaustive key search
Modern & Applied Cryptography Breakers Intermediate

Breaking DES with Brute-Force Key Search

DES never fell to clever math. It fell to a loop: try a key, encrypt a known block, compare, repeat. This post runs that exact loop against real DES, the same one EFF's Deep Crack ran over all 2⁵⁶ keys in 1998.

18 min read

A visual representation of an MD5 hash collision
Modern & Applied Cryptography Breakers Intermediate

Breaking MD5 with Collision Attacks

Every hash function is vulnerable to a generic birthday attack. MD5 is vulnerable to something worse: a real, structural flaw that produces full 128-bit collisions far faster than any generic attack should allow. Both are demonstrated here, live and verified.

16 min read

A visual representation of the RC4 second-byte keystream bias
Modern & Applied Cryptography Breakers Intermediate

Breaking RC4 with Its Second-Byte Bias

RC4's second keystream byte is zero twice as often as it should be. Encrypt the same secret enough times, under any keys at all, and that one flaw hands the secret's second byte straight to anyone watching the ciphertexts.

12 min read

A visual representation of breaking Diffie-Hellman via baby-step giant-step
Modern & Applied Cryptography Breakers Intermediate

Breaking Diffie-Hellman with Baby-Step Giant-Step

Diffie-Hellman's security rests on the discrete logarithm problem being hard. For a small prime, it isn't. Baby-step giant-step trades a brute-force search of size p for one of roughly √p, and that's the whole reason real DH needs huge safe primes.

11 min read

A visual representation of breaking ElGamal via the discrete logarithm
Modern & Applied Cryptography Breakers Intermediate

Breaking ElGamal with Baby-Step Giant-Step

ElGamal's private key is just another discrete logarithm. The same baby-step giant-step technique that breaks Diffie-Hellman over a small prime recovers ElGamal's private key too, and from there decrypts any captured ciphertext directly.

11 min read

A visual representation of breaking RSA via Håstad's broadcast attack
Modern & Applied Cryptography Breakers Intermediate

Breaking RSA with Håstad's Broadcast Attack

A low public exponent like e=3 is efficient and, by itself, still safe. Broadcast the same message to three recipients using e=3 with no padding, and the Chinese Remainder Theorem recovers it with no private key at all.

10 min read

A visual representation of breaking RSA via the common modulus attack
Modern & Applied Cryptography Breakers Intermediate

Breaking RSA with the Common Modulus Attack

Sharing one RSA modulus across multiple key pairs looks like a harmless shortcut: skip prime generation, reuse n. If the same message ever gets encrypted under two of those keys, no private key is needed to read it back.

13 min read

A visual representation of breaking RSA via Fermat factorization
Modern & Applied Cryptography Breakers Intermediate

Breaking RSA with Fermat Factorization

RSA's security assumes factoring n back into p and q is infeasible. That assumption quietly breaks if the key generator picks p and q too close together. Fermat's 1643 factoring method recovers them both in seconds.

13 min read

A visual representation of breaking RSA via Wiener's attack
Modern & Applied Cryptography Breakers Advanced

Breaking RSA with Wiener's Attack

Small private exponents make RSA decryption and signing faster. Michael Wiener showed in 1990 that a d small enough to help performance is also small enough to recover from the public key alone, via continued fractions.

12 min read

A visual representation of breaking the Autokey Cipher
Basic Classic Symmetric Breakers Intermediate

Breaking the Autokey Cipher

The Autokey cipher defeats Kasiski examination and the Index of Coincidence by never repeating its key. But the short priming key that starts everything off is still just a handful of letters, and one wrong guess collapses the entire decryption for you.

34 min read

A visual representation of the Turing/Welchman Bombe breaking Enigma
Basic Classic Symmetric Breakers Advanced

Breaking Enigma the Real Way: The Turing/Welchman Bombe

The site's simplified Enigma breaker fixes the rotor order, skips the plugboard, and brute-forces 17,576 positions by statistics. The real Bombe did none of that. It searched rotor order and position too, deduced the plugboard through pure logic, and never scored a single decryption.

34 min read

A visual representation of breaking the Hill Cipher
Basic Classic Symmetric Breakers Intermediate

Breaking the Hill Cipher

Every other breaker on this site attacks ciphertext alone, guessing at a key through brute force or statistical search. The Hill cipher doesn't need any of that. Its encryption is pure linear algebra, so a handful of known plaintext letters is enough to solve for the entire key matrix directly.

16 min read

A visual representation of breaking the Playfair Cipher
Basic Classic Symmetric Breakers Advanced

Breaking the Playfair Cipher

Playfair defeated single-letter frequency analysis by encrypting pairs of letters through a 5×5 key square. But the same simulated-annealing idea that cracks the substitution cipher still works here too, once you swap in quadgram statistics and a richer set of moves.

20 min read

A visual representation of breaking the Rail Fence Cipher
Basic Classic Symmetric Breakers Beginner

Breaking the Rail Fence Cipher

Every other transposition breaker on this site has to search over orderings. Columnar Transposition alone hides a factorial number of column arrangements behind its key. Rail Fence has no such trapdoor: the entire key is a single small number, so brute force checks every possibility outright.

14 min read
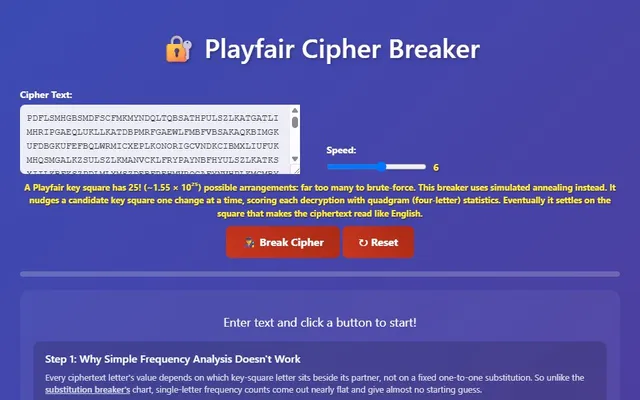
A visual representation of breaking the Affine Cipher
Basic Classic Symmetric Breakers Beginner

Breaking the Affine Cipher

Learn how to break the Affine cipher by brute-forcing its entire 312-key keyspace and scoring each decryption with a common-word heuristic. It's the same strategy that cracks Caesar, just applied to a slightly bigger lock.

15 min read
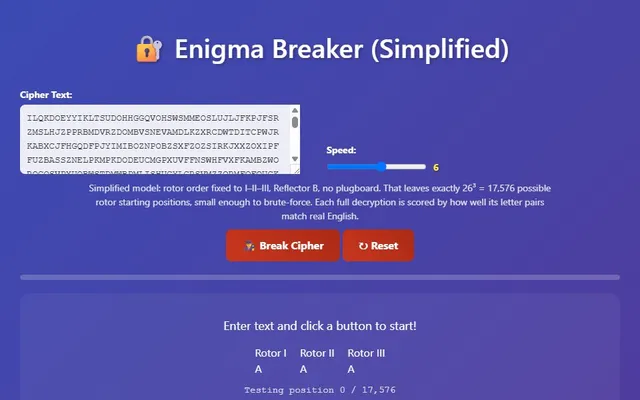
A visual representation of breaking the Beaufort Cipher
Basic Classic Symmetric Breakers Intermediate

Breaking the Beaufort Cipher

The Beaufort cipher's reciprocal formula (C = K − P instead of Vigenère's C = P + K) looks like it should matter to an attacker. It doesn't: the same Kasiski examination, Index of Coincidence, and chi-squared pipeline that breaks Vigenère breaks Beaufort just as cleanly.

16 min read
A visual representation of breaking the Columnar Transposition Cipher
Basic Classic Symmetric Breakers Intermediate

Breaking the Columnar Transposition Cipher

Columnar transposition doesn't hide letters. It just rearranges them, so frequency analysis finds nothing wrong. Learn the attack that actually works: brute-forcing every column order for each candidate key length, scored by common English substrings.

18 min read
A visual representation of breaking a simplified Enigma machine
Basic Classic Symmetric Breakers Advanced

Breaking a Simplified Enigma Machine

The real wartime Enigma resisted brute force because of two unknowns stacked on top of its rotor positions: which three rotors were chosen and in what order, and how the plugboard was wired. Together these push the key space past 10^20. Strip those two unknowns away and only 17,576 rotor positions are left, small enough for a modern computer to brute-force outright.

27 min read
A visual representation of breaking the monoalphabetic Substitution Cipher
Basic Classic Symmetric Breakers Advanced

Breaking the Substitution Cipher

A monoalphabetic substitution key is one arbitrary permutation of 26 letters: 26! of them, far too many to brute force and immune to Kasiski or the Index of Coincidence since there's no repeating key. Here's how frequency analysis and a hill-climbing search crack it anyway.

26 min read

A visual representation of the Vigenère Cipher Algorithm Breaker
Basic Classic Symmetric Breakers Intermediate

The Vigenère Cipher Breaking Guide

For three centuries the Vigenère cipher was called 'le chiffre indéchiffrable.' Learn the two statistical techniques, Kasiski examination and the Index of Coincidence, that finally broke it, and watch them recover a real key letter by letter.

17 min read

Breaking the Caesar Cipher with A Python Script
Basic Classic Symmetric Breakers Beginner

The Caesar Cipher Breaking Guide

Breaking the Caesar Cipher: A Python Journey from Comprehensive to Concise

15 min read

← All tags