Cipher Visualizers home

Tag

#ECC

2 articles with this tag.

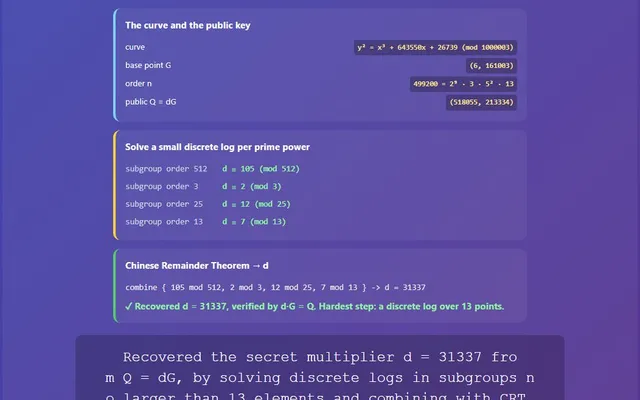
A visual representation of Pohlig-Hellman splitting an elliptic curve discrete log into small subgroups and combining with CRT
Modern & Applied Cryptography Breakers Advanced

Breaking Toy ECC with Pohlig-Hellman

Elliptic curve security does not come from the size of the field. It comes from one number: the largest prime factor of the group order. When that order is smooth, Pohlig-Hellman splits the discrete log into tiny subgroups and solves it in a flash. This guide runs the real attack on a toy curve and recovers the private key.

13 min read
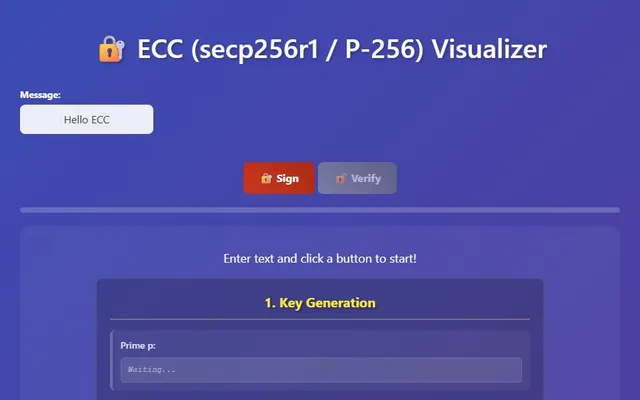
A visual representation of the ECC Protocol.
Modern Asymmetric Algorithms Advanced

Elliptic Curve Cryptography

ECC gets RSA-level security from far smaller keys. Here's the curve math behind it, and why it now powers most of the web.

13 min read

← All tags