Modern & Applied Cryptography Breakers Advanced
Breaking RSA with Weak Keys: Shared Primes and Pollard's p-1
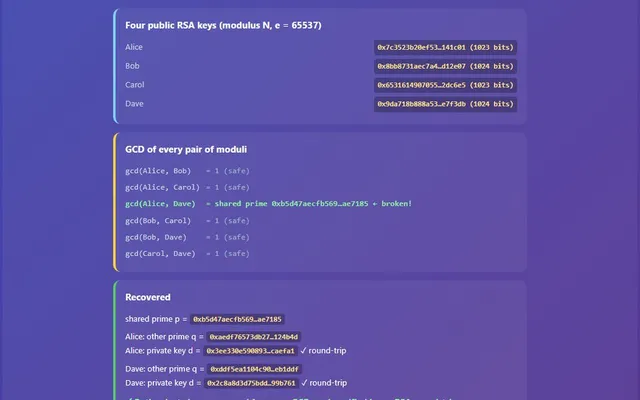
RSA is unbreakable only when its primes are chosen well. If two keys share a prime, one GCD factors both in microseconds, and if a prime p has a smooth p-1, Pollard's method factors it without any search. This guide runs both real attacks against real 1024-bit keys and recovers the private keys.
11 min read